Security and compliance

Trust Centre

At Implement AI we treat security and data protection as core product features, not add ons. This Trust Centre explains how we protect customer data and shows the certifications and controls that support our approach.

Certifications

The certifications behind our approach.

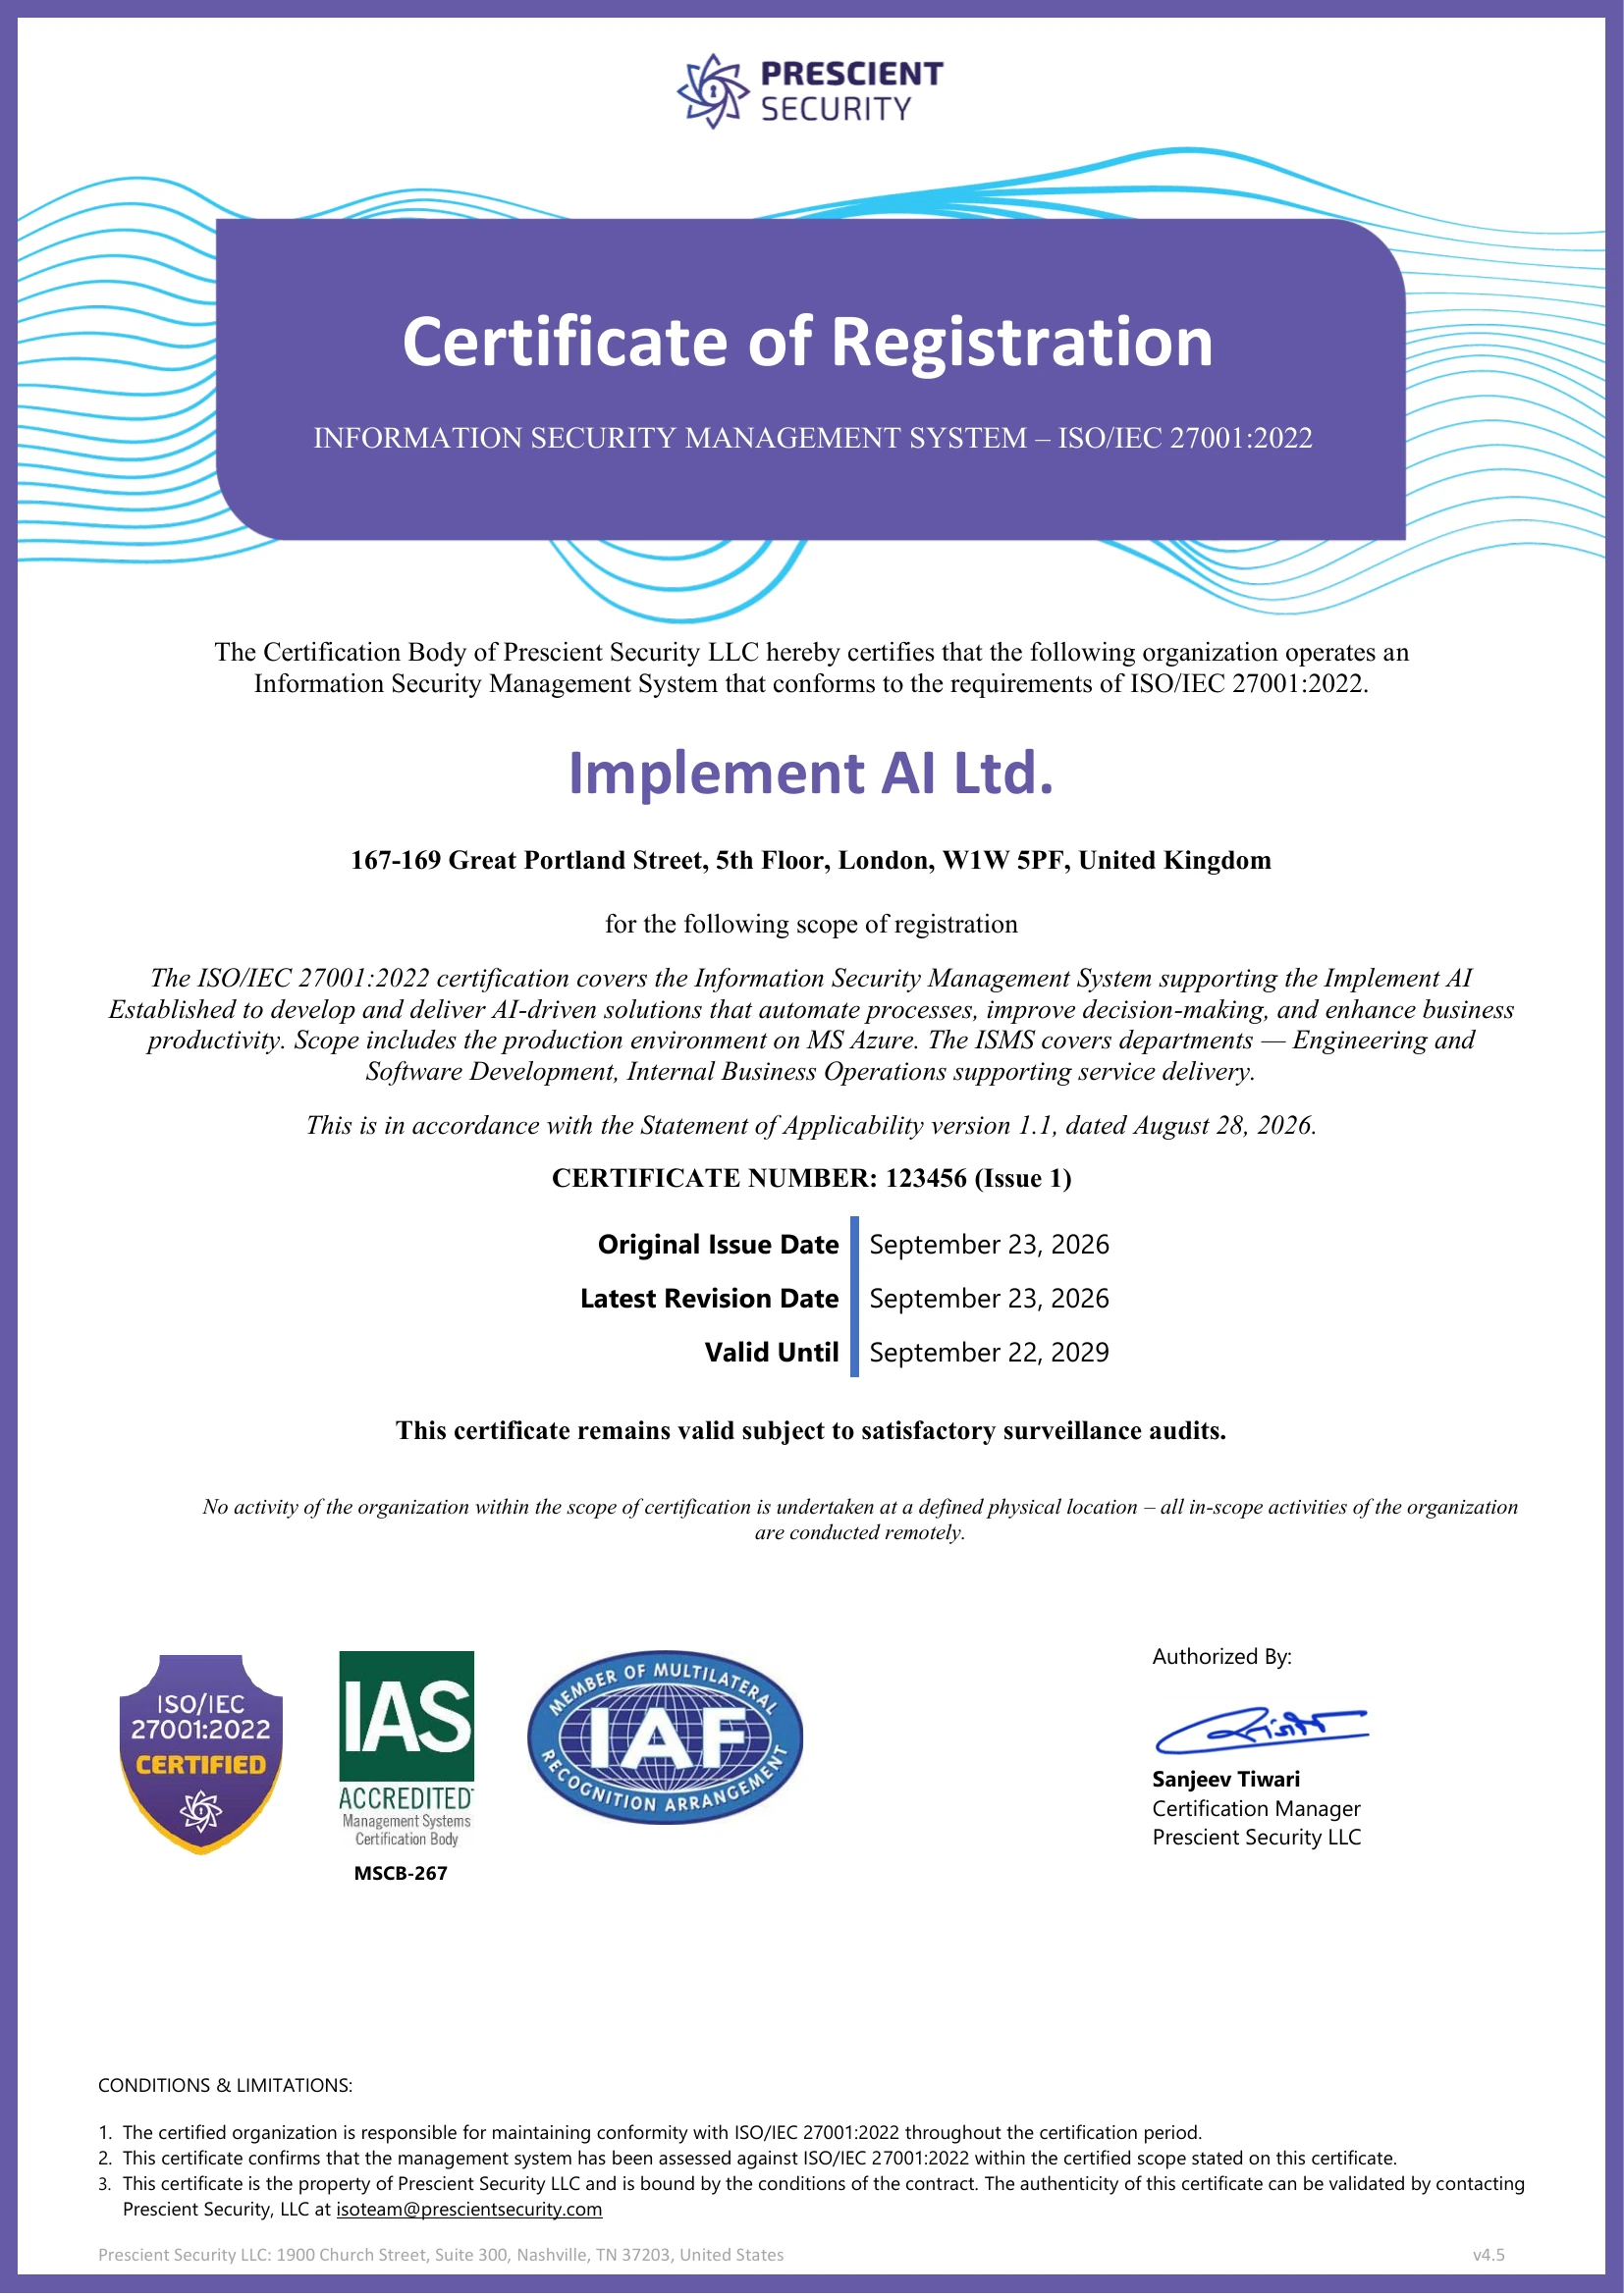
ISO/IEC 27001:2022 Certified

ISO/IEC 27001:2022 Certification

Our Information Security Management System is certified to ISO/IEC 27001:2022.

  • Certification body: Prescient Security
  • Certificate no.: 123456 (Issue 1)
  • Scope: Engineering & Software Development and Internal Business Operations, with production on MS Azure
  • Original issue date: 23 September 2026
  • Valid until: 22 September 2029, subject to satisfactory surveillance audits

Implement AI Ltd. operates an Information Security Management System certified to ISO/IEC 27001:2022 by Prescient Security (Certificate no. 123456).
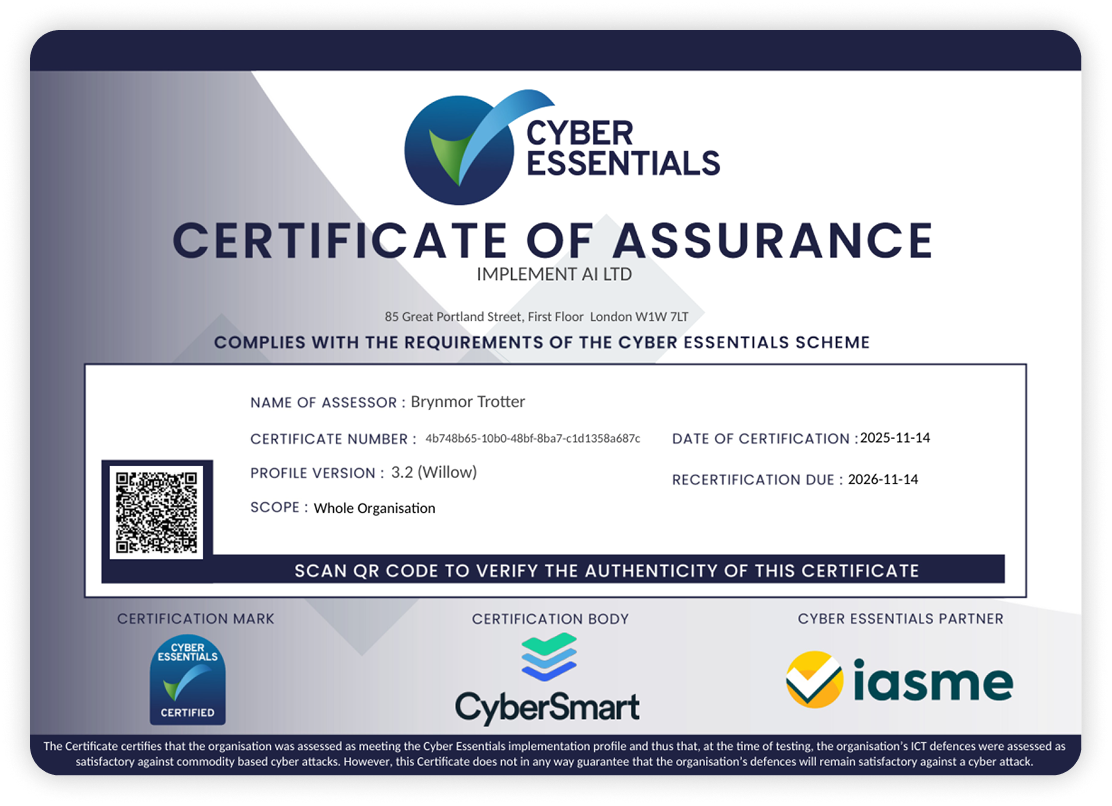
Cyber Essentials Certified

Cyber Essentials Certification

Our current certificate confirms that:

  • Organisation name: Implement AI Ltd
  • Scope: Whole organisation
  • Profile version: 3.2 Willow
  • Date of certification: 14 November 2025
  • Recertification due: 14 November 2026
NHS Data Security and Protection Toolkit: Standards Met 2026–27

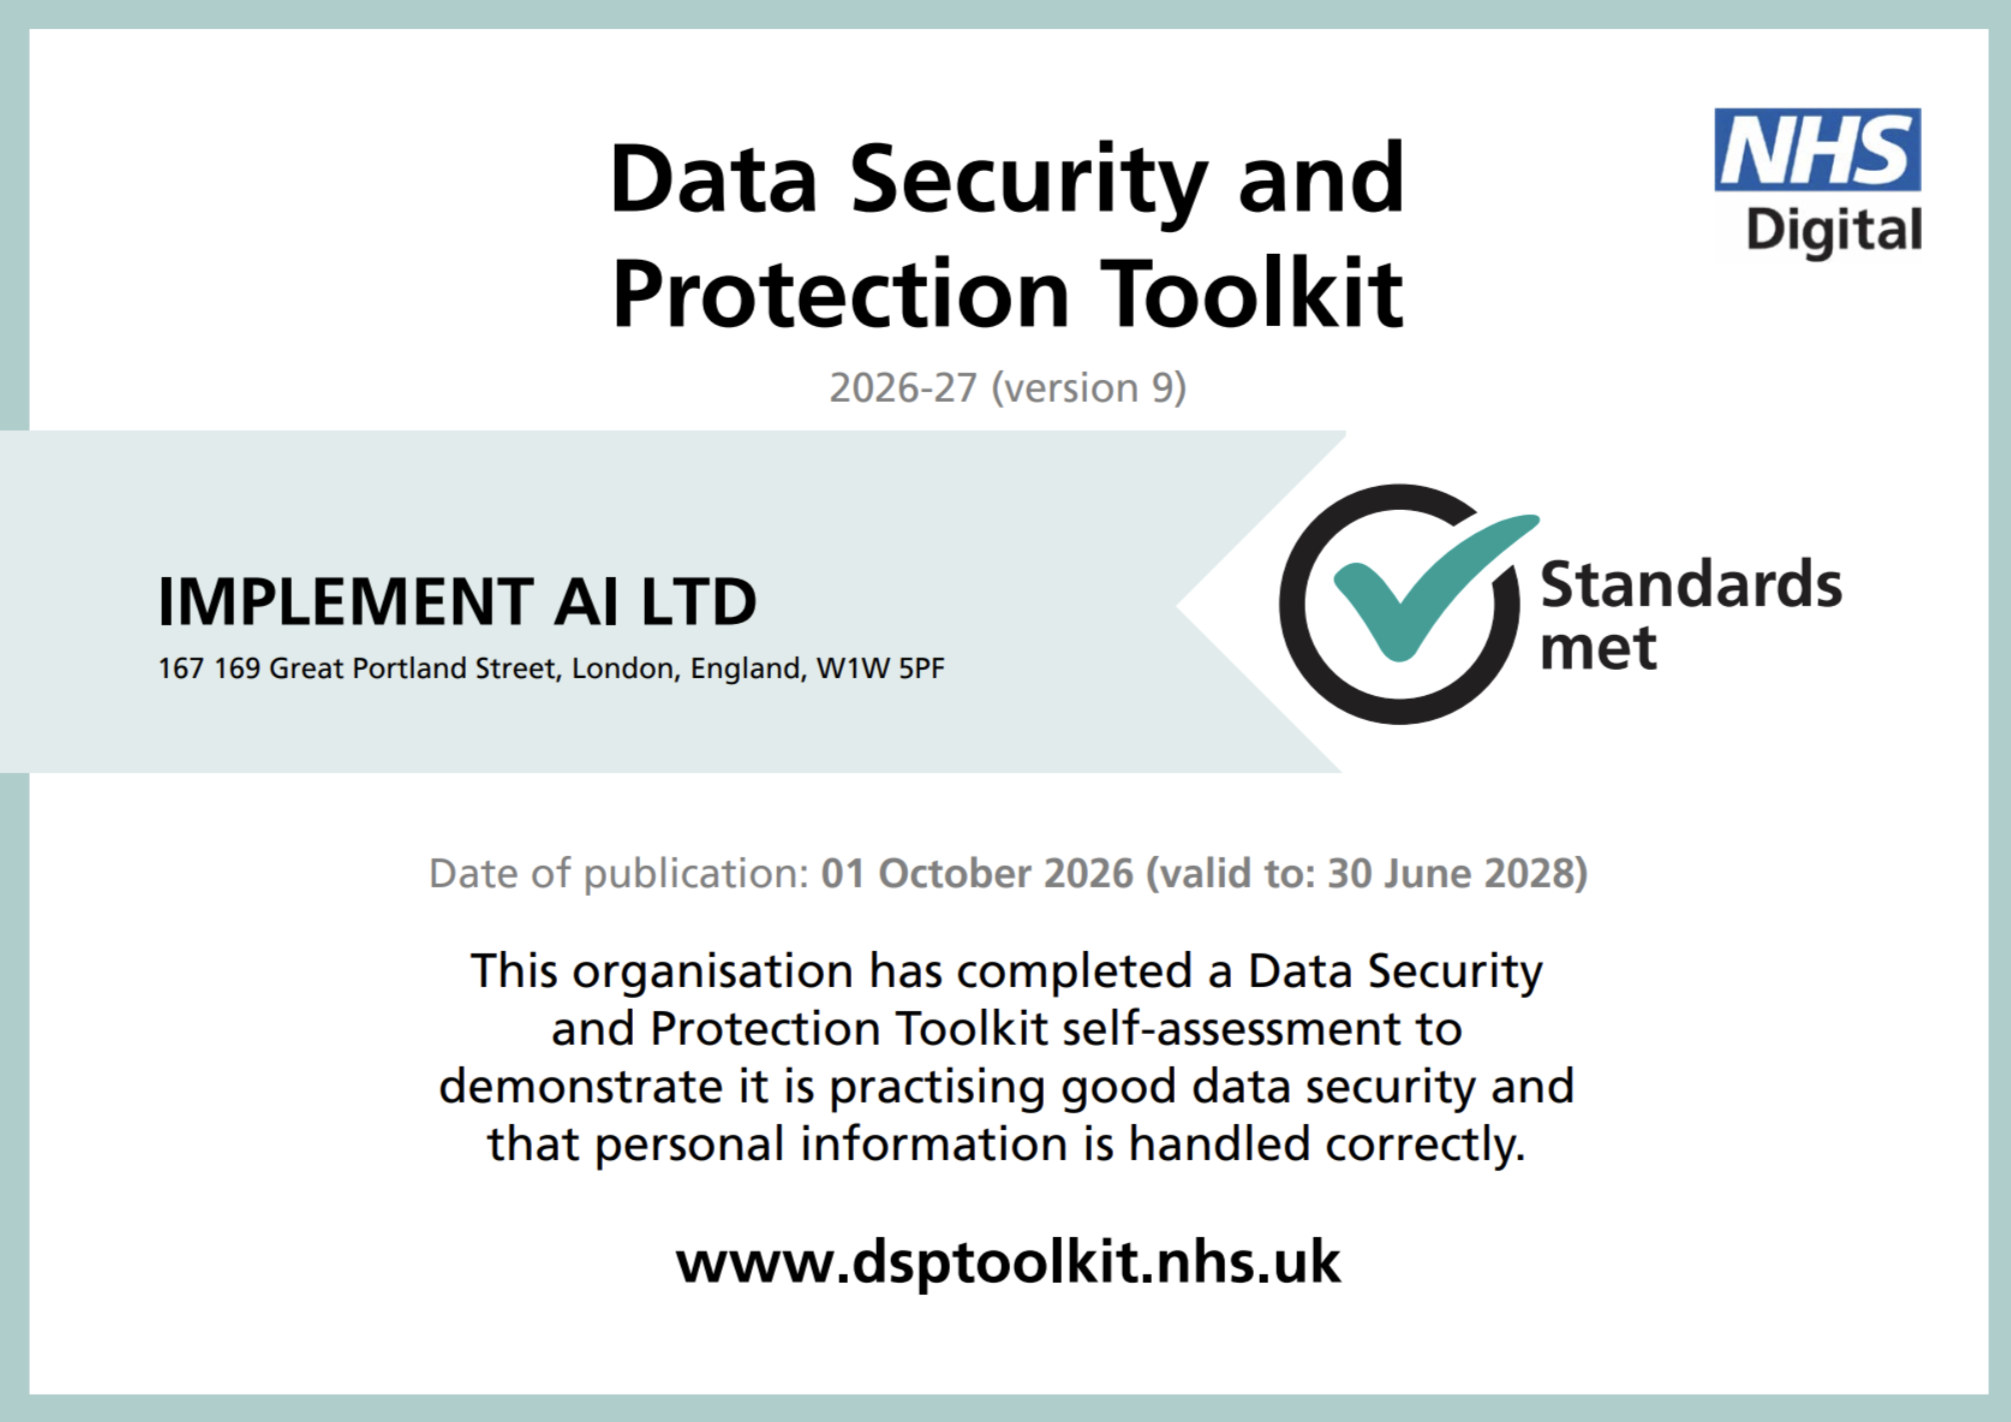
NHS Data Security and Protection Toolkit

Implement AI Ltd. has published a 2026–27 NHS Data Security and Protection Toolkit self-assessment with Standards Met status.

  • Status: Standards met
  • Toolkit: 2026-27 (version 9)
  • Date of publication: 01 October 2026
  • Valid to: 30 June 2028
How we protect your data

Information Security Overview

We design our platform and internal processes so that security is built in by default. At a high level this includes:

  • All data stored and processed only in Azure UK regions for full UK GDPR compliance.
  • No routine international transfer; AI providers receive masked, minimal data with no retention.
  • Encryption by default: AES-256 at rest, TLS 1.2+ in transit.
  • Strict access control: MFA, RBAC, and no access for non-operational staff.
  • Full audit logging of access and admin actions, retained 12 months.
  • Segregated environments for dev, test, and production.
  • Azure-grade physical and network security including firewalls and WAF.
  • Privacy by design with GDPR-compliant DPA and documented data flows.
  • Controlled retention and secure deletion, including certificates on request.
  • EU AI Act and OWASP compliance across our platform and AI development.
  • Assurance roadmap: Cyber Essentials Plus and ISO/IEC 42001 underway; SOC 2 in audit phase.

These measures are supported by documented policies, regular reviews, and ongoing security awareness across the organisation.

Cyber insurance

Cyber Insurance Coverage

In addition to our Cyber Essentials certification, Implement AI maintains comprehensive cyber insurance cover aligned with industry standards. This supports incident response, business continuity, and risk management should a security event occur.

Details are available on request where required for due diligence purposes.

Find your highest impact use cases.

Chat or talk to Ava